How to install and configure Sentinel Firewall on Ubuntu 24.04
Sentinel is a popular VPS security tool for Linux. It provides a simple interface for iptables to protect Linux servers. Sentinel comes with multiple features: a stateful packet inspection firewall (SPI), intrusion detection, a login failure daemon, DDOS protection, and control panel integration. This tutorial covers installation, basic configuration, and essential commands for CSF on Ubuntu 24.04.
1. Deploy Ubuntu Server
- Deploy a new Ubuntu 24.04 VPS instance.
- Connect to the server via SSH as root.
2. Prepare for Sentinel
Ubuntu 24.04 comes with the UFW firewall by default, which must be removed before installing Sentinel.
apt remove ufwInstall the dependenciesČ
apt install perl zip unzip libwww-perl liblwp-protocol-https-perlSendmail is required to send alerts to the administrator:
apt install sendmail-bin3. Install Sentinel
- Change to
/usr/srccd /usr/src - Download the latest Sentinel from GitHub:
wget https://github.com/sentinelfirewall/sentinel/raw/refs/heads/main/csf.tgz - Extract CSF:
tar -xzf csf.tgz - Change to
/usr/src/csfcd csf - Run the install script:
sh install.sh - Verify the required iptables modules for CSF are available:
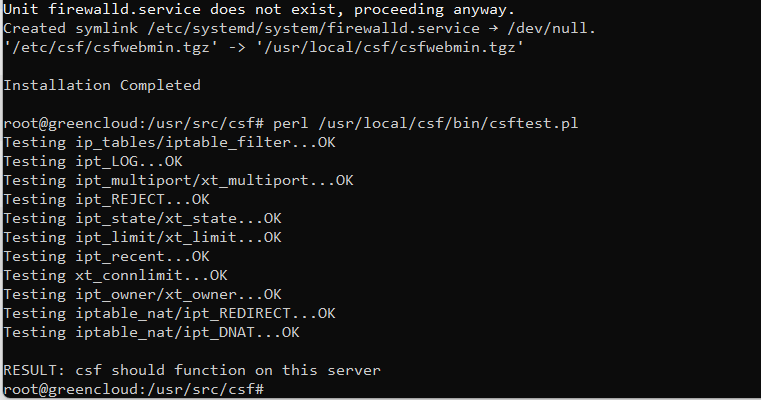
perl /usr/local/csf/bin/csftest.plConfirm that all tests report OK, and you see the following result.

- Verify CSF status after installation.
csf -vYou should see a result similar to:


4. Configure Firewall
- CSF runs in TESTING mode by default. Edit
/etc/csf/csf.confto disable the TESTING mode:
nano /etc/csf/csf.confLocate the line TESTING = "1", and change the value to “0“.
TESTING = "0"- Locate the line
RESTRICT_SYSLOG = "0", and change the value to “3“. This means only members of theRESTRICT_SYSLOG_GROUPmay access syslog/rsyslog files. More information
RESTRICT_SYSLOG = "3"Save the configuration file.
3. Stop and reload CSF with the -ra option.
csf -ra4. Common Commands & Configuration
Start CSF
csf -s Stop CSF
csf -f Restart CSF
You must restart CSF each time the configuration file changes.
csf -ra Allow IP traffic by port
Edit /etc/csf/csf.conf
nano /etc/csf/csf.confLocate the following lines and add the required ports:
# Allow incoming TCP ports
TCP_IN = 20,21,22,25,26,53,80,110,143,443,465,587,993,995,2077”

# Allow outgoing TCP ports
TCP_OUT = 20,21,22,25,26,37,43,53,80,110,113,443,465,873,2087”
Restart CSF for the changes to take effect.
csf -raAllow or deny by IP address
Use the -d option to deny by IP, for example, 192.0.2.123.
csf -d 192.0.2.123Use the -a option to allow by IP, for example, 192.0.2.123.
csf -a 192.0.2.123Remove IP from the allow list.
csf -ar 192.0.2.123Remove IP from the deny list.
csf -dr 192.0.2.123Deny file
Block IPs by adding an entry to /etc/csf/csf.deny:
192.0.2.123     # deny this IP
192.0.2.0/24    # deny this network
Allow file
Add trusted IPs to /etc/csf/csf.allow:
192.0.2.123 # trust this IP
Check all listening ports with the -p option:
csf -pMore Information
For more information about VPS security, see the Documentation.
