How to Resolve passwd: Module is unknown on RHEL
Introduction
On RHEL, the passwd command can fail with errors like:
passwd: Module is unknown
or
passwd: Authentication token manipulation error
These errors usually occur because of missing or corrupted PAM modules, misconfigured PAM configuration files, or security restrictions like SELinux. This guide provides a detailed, step-by-step approach to fixing these issues.
Step 1: Check SELinux Status
First, check the SELinux mode:
-
Output can be Enforcing, Permissive, or Disabled.
-
If
Enforcing, SELinux may block PAM modules from loading.
Temporarily set SELinux to permissive mode:
Remember to restore SELinux to its original mode after troubleshooting.
Step 2: Check PAM Configuration Files
Inspect the main PAM configuration files:
ls -l /etc/pam.d/passwd /etc/pam.d/system-auth /etc/pam.d/password-auth
cat /etc/pam.d/passwd
-
Ensure the files exist.
-
Ownership should be root: root, permissions 644.
-
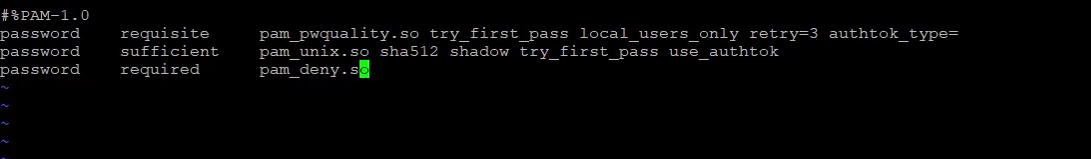
Standard
/etc/pam.d/passwdcontent:
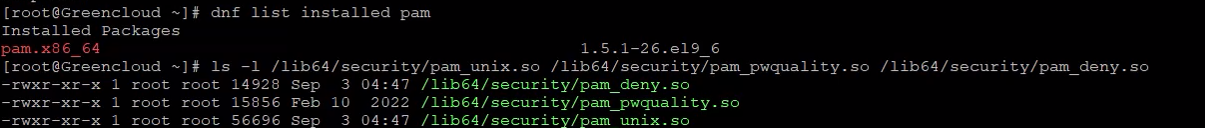
Step 3: Check Critical PAM Modules
Check that essential PAM modules exist:
-
pam_unix.so: handles authentication and password changes -
pam_pwquality.so: enforces password policies -
pam_deny.so: ensures denial rules are enforced
Test password change:
passwd
-
If successful, the modules are working.
-
If errors persist, modules may be missing or corrupted.
Step 4: Verify or Reinstall PAM
Check if PAM is installed:
dnf list installed pam
-
If installed, reinstall to restore missing or corrupted modules:
-
If not installed, install PAM:
dnf install libpwquality

After installation, recheck critical modules:
Test password change again:
Step 5: Restore PAM Configuration Files (if needed)
Backup existing configuration:
cp -a /etc/pam.d/ /root/pam.d
-a preserves permissions, ownership, and directory structure.

Restore standard configuration: /etc/pam.d/passwd
vi /etc/pam.d/passwd
Delete existing content and enter the standard configuration:
Set Correct Permissions and Ownership:
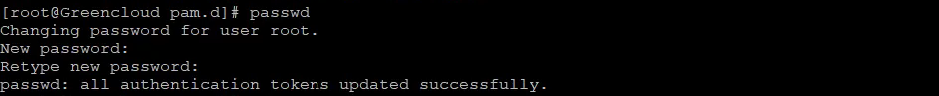
Step 6: Verify and Restore
-
Test password again:
passwd
-
Check configuration files:
-
Restore SELinux if changed:
setenforce 1 # if originally Enforcing getenforce
Conclusion
Following these steps ensures:
-
SELinux is temporarily permissive for troubleshooting.
-
PAM configuration files are correct and have proper permissions.
-
Critical PAM modules exist and function.
-
PAM package is installed or reinstalled if missing or corrupted.
-
Password changes work correctly on the system.
Always test these steps in a safe environment before applying to production systems.
